Loading
Latest posts
 Your Intune Compliance Is Moving to Azure Attestation… and Your Firewall Might Break it
 Microsoft is Unifying the Copilot Apps… What IT Admins need to know before September 2026
 Remove Device Everywhere – Because Microsoft Thought 3 Portals Was a Good Idea
 I Asked Copilot To Make ASCII Art… and It Broke My Soul
 AZ-140 Renewal 2025 – What Microsoft Really Tested (and what they didn’t)
Related posts
- Your Intune Compliance Is Moving to Azure Attestation… and Your Firewall Might Break it
- Microsoft is Unifying the Copilot Apps… What IT Admins need to know before September 2026
- Remove Device Everywhere – Because Microsoft Thought 3 Portals Was a Good Idea
- I Asked Copilot To Make ASCII Art… and It Broke My Soul
- AZ-140 Renewal 2025 – What Microsoft Really Tested (and what they didn’t)
Microsoft Exchange: The NSA, the CISA, and the Race Against End-of-Life
 Engin Soysal
Hey You,
If you’re still running an on-prem Exchange Server in 2025, first of all… congratulations. You’re officially on a government watchlist.

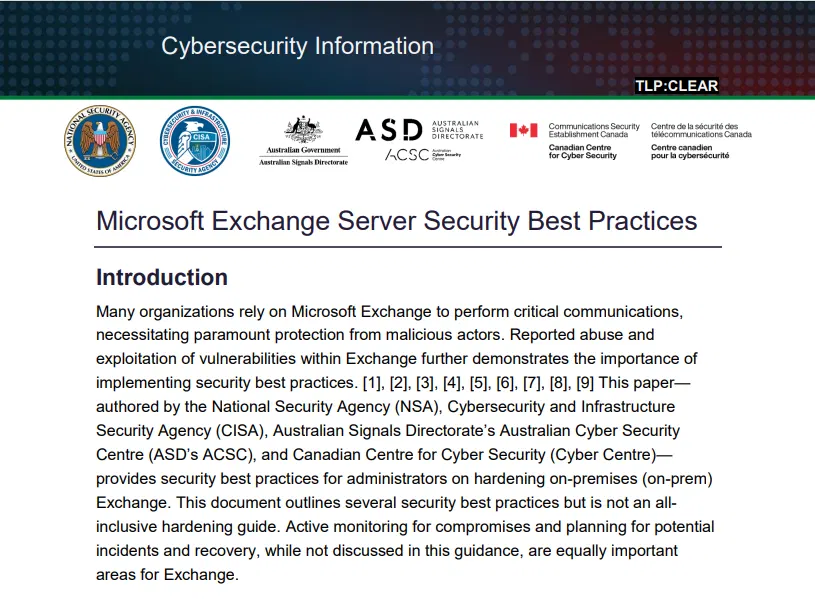
Okay, maybe not literally, but according to a new joint report by the NSA, CISA, ASD and the Canadian Cyber Centre, your Exchange server is under imminent threat. And they’re not joking.
The 24-page paper called “Microsoft Exchange Server Security Best Practices” just dropped and it’s basically a wake-up call for anyone who thought “We’ll patch it next week” was still a valid IT strategy.
Let’s go over wat actually matters.
1. Keep it updated (like… yesterday)
Use:
They’re free. They work and they’ll save you from a weekend incident response call.
2. Migrate or Die (figuratively)
As of October 14th, 2025, Exchange 2016 and 2019 are officially End-Of-Life. Microsoft’s message is clear: move to Exchange Server SE or Microsoft 365.
Still need time? Fine… just isolate that box from the internet, lock it down and let it quietly retire in a network corner.
No internet… no exposure… simple math.
3. Keep the EM service alive
Microsoft’s Exchange Emergeny Mitigation (EM) service applies temporary fixed automatically through the Office Config Service. Think of it as Exchange’s “defibrillator”… not a cure… but it can keep you alive until the doctor (patch) arrives.
4. Apply baselines
CIS Benchmarks®, DISA STIGs, Microsoft Security Baselines… pick one.
Baseline = Known good
No baseline = guesswork
Guesswork + exchange = breach.
5. Built-in protection exists (use it)
You already have:
So, turn them on.
Bonus: block webshell creation with ASR. If that doesn’t sound cool… you’ve never been hacked.
6. Kill NTLM before it kills you.
NTLM is finally on life support. Start auditing and migrating to Kerberos now.
The new Exchange Server SE (CU1) will replace NTLMv2 with Kerberos by default… so this is not optional.
7. Modern Auth or Bust
Basic Authentication is dead. Use Modern AUTH + MFA (OAuth 2.0 via ADFS or Entra ID).
It’s more secure… and honestly… if you’re still typing passwords in plain text in 2025… you DESERVE every phishing mail you get.
8. Encrypt EVERYTHING
- TLS everywhere (inside and out)
- Enable HSTS
- Use Extended Protection (EP) to stop token relay attacks
- And yes… restart the damn server after changing TLS configs. I know you won’t but now you can’t say you didn’t know.
9. Role separation & Split permissions
Stop using Domain Admin accounts to manage Exchange. I will repeat… STOP USING THE DAMN DOMAIN ADMIN ACCOUNTS…
RBAC exists for a reason… use it. If exchange gets compromised, it shouldn’t take down your ENTIRE AD FOREST with it.
10. Zero Trust… or… Zero Chance
Every line of the NSA reports screams ZERO TRUST:
- Assume breach.
- Verify explicity.
- Minimize blast radius
Translation: Stop trusting everything inside your LAN.
TL;DR… your next steps
- Patch everything
- Plan your migration to Exchange SE of M365
- Enable EM Service
- Turn on built-in protections
- Get rid of NTLM
- Use Modern AUTH + MFA
- Lock down admin access
- Embrace zero trust
Because honestly, if the NSA, CISA, ASD and Canada are all writing one document… together… you might want to take the hint.

Thanks for reading.
Cheers,
Engin
 Engin Soysal
Microsoft MVP and Microsoft Certified Trainer, sharing practical experience with Azure, Microsoft Intune and endpoint engineering.
43 stories · read them all
0 Comments